
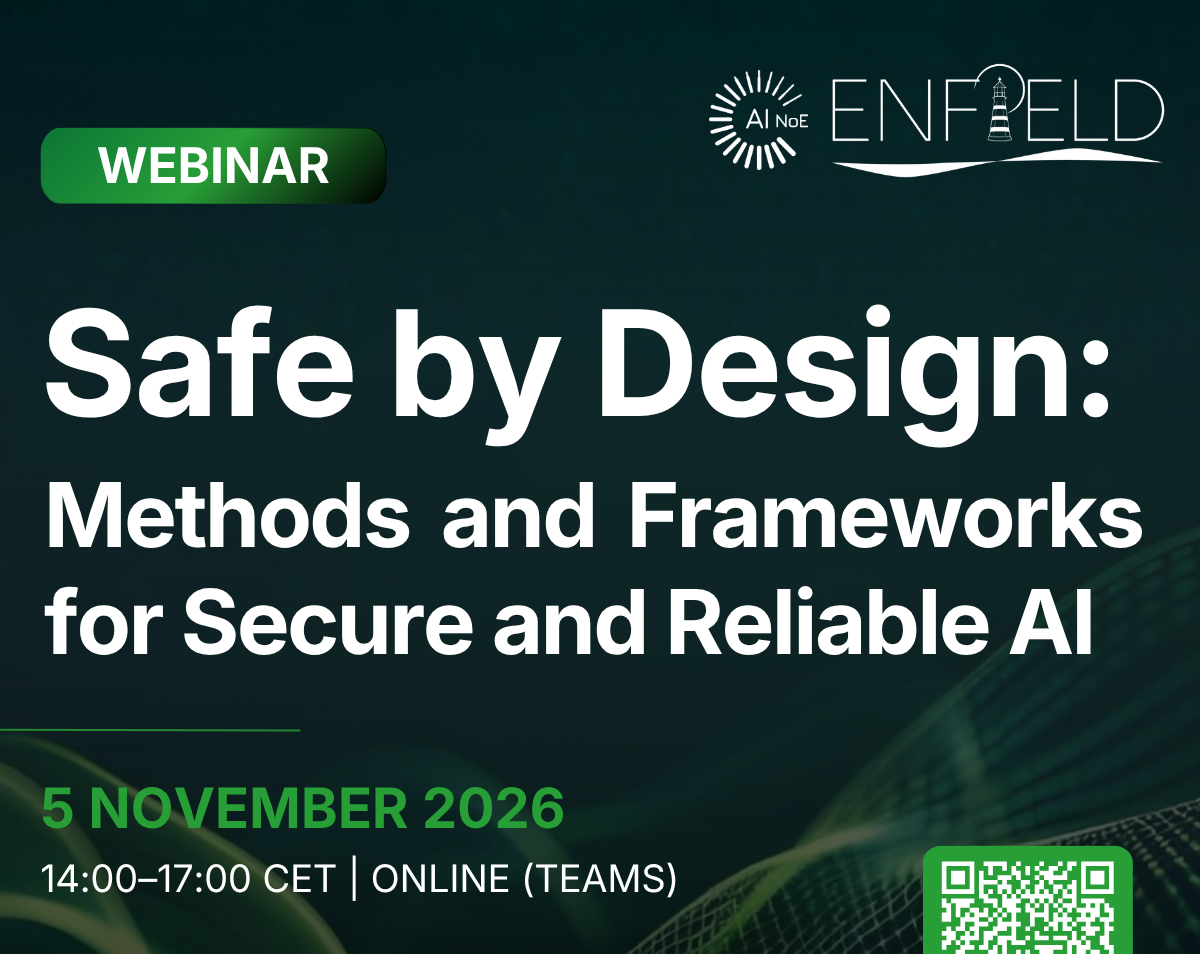
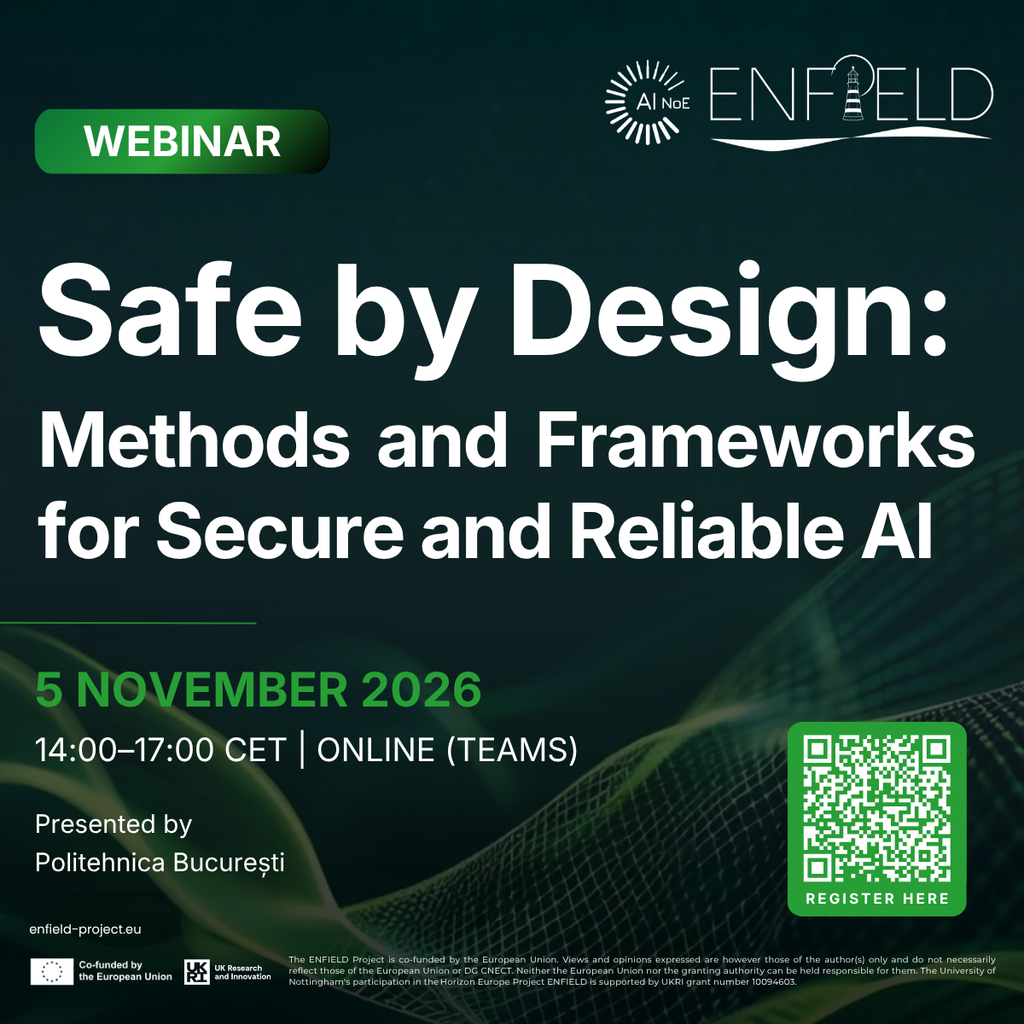
Webinar Safe by Design: Methods and Frameworks for Secure and Reliable AI
Artificial Intelligence is now part of everyday life, from the services we use and the decisions that affect us to the infrastructure our societies depend on. Like many disruptive technologies, it brings both real benefits and real risks. As AI incidents and hazards become more frequent, a shared question arises for everyone who builds, buys, regulates, or is affected by AI: how can we make sure these systems are safe, secure, and worthy of trust?
Answering this question is hard. AI systems are evolving quickly and growing more complex. Their key assets, such as data and models, face a widening range of threats. Safety itself has many dimensions, including physical, ethical, societal, and environmental ones, and it must stay aligned with human values. Moreover, hundreds of fragmented and non-standardized methods and tools already exist. That makes it difficult for organizations and individuals to know where to start.
This webinar offers a view of AI safety and security, dedicated to a broad audience: AI developers and researchers, managers and decision-makers, public-sector professionals and policymakers, and students and citizens interested in how trustworthy AI is built and governed.
The main topics of the webinar will be:
- Building safety in from the start: principles and good practices for designing, developing, and deploying secure and reliable AI systems, and how different stakeholders contribute to them
- Assessing AI risks in practice: frameworks, tools, and metrics for identifying and evaluating risks, illustrated with real-world case studies
- AI safety and security under the EU AI Act: what the regulation requires, and what it means for organizations that develop or use AI.
Participants will leave with an understanding of the main challenges and practical steps that make “safe by design” achievable. The webinar is organized within the Horizon Europe project ENFIELD, the European Lighthouse to Manifest Trustworthy and Green AI.
Participation is free!
Date: 05 November 2026, 14:00-17:00 CET
Location: Online (Teams)
To join, you must access the following link.
Speakers
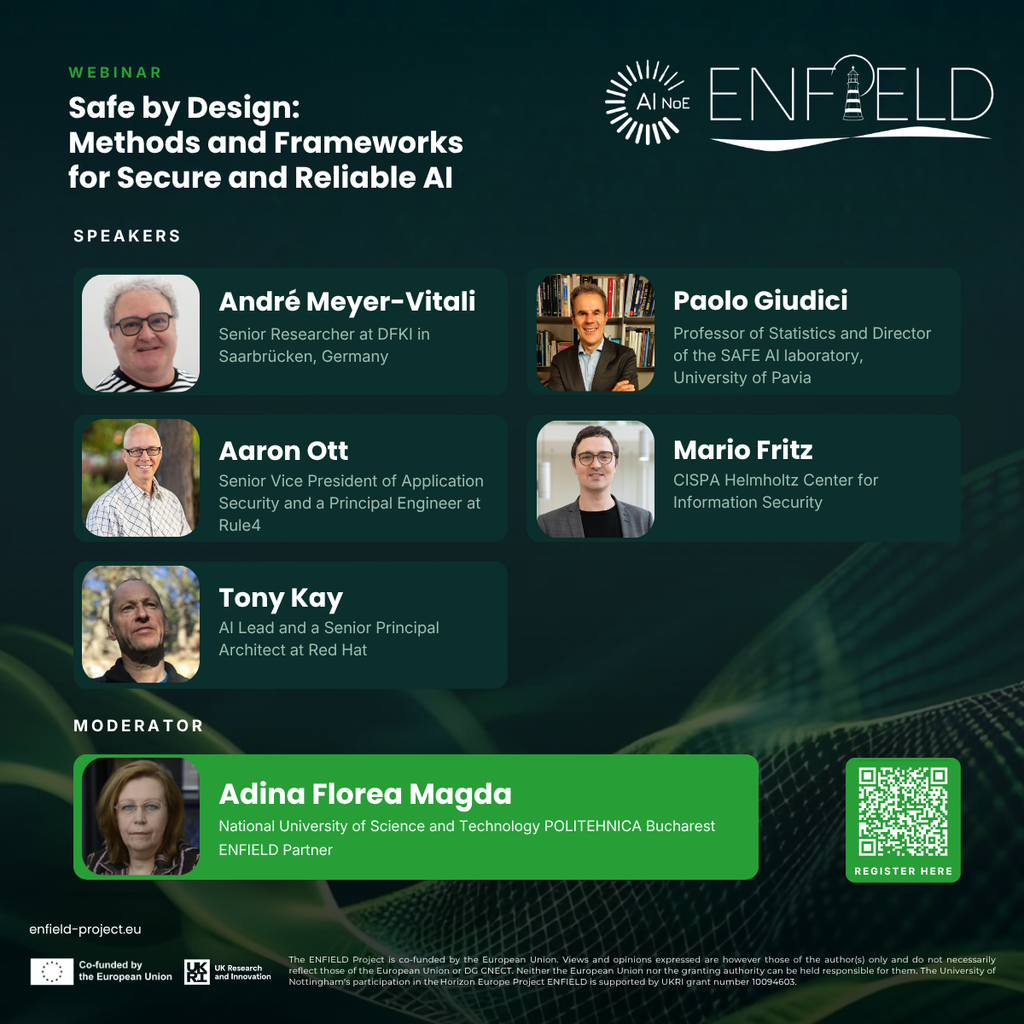
André Meyer-Vitali Senior Researcher at DFKI in Saarbrücken, Germany
Aaron Ott
Sr. Vice President of Application Security and a Principal Engineer at Rule4
Tony Kay
AI Lead and a Senior Principal Architect at Red Hat
Paolo Giudici Professor of Statistics and Director of the SAFE AI laboratory, University of Pavia
Mario Fritz
CISPA Helmholtz Center for Information Security
Program
| Date 5 November 2026, 14:00-17:00 CET | Presentations |
| Tell Me Why! Creating Trust in AI Sytems by Design. André Meyer-Vitali,Senior Researcher at Deutsches Forschungszentrum für Künstliche Intelligenz (DFKI) in Saarbrücken, Germany | |
| S.A.F.E. AI metrics. Paolo Giudici, Professor of Statistics and Director of the SAFE AI laboratory, University of Pavia | |
| When “Safer” is the Exploit: What AI Agent Failures Teach Us About Trustworthy AI. Aaron Ott, Senior Vice President of Application Security and a Principal Engineer at Rule4 | |
| Cybersecurity of AI and Cybersecurity with AI – Past, Present, Future. Mario Fritz, CISPA Helmholtz Center for Information Security | |
| Security meets AI — has the landscape changed forever? Tony Kay, AI Lead and a Senior Principal Architect at Red Hat | |
| Q&A Session |
Target audience
The target audience includes researchers, engineers, students, and professionals interested in the application of AI.
Registration
Don’t miss this opportunity! Participation is free.
- When: 11 November 2026, 14:00-17:00 CET
- Where: Online
To join, you must access the following link.
Check the ENFIELD previous webinars: